Find out what your control network is really doing.
Operational technology and industrial control systems security advisory for pipeline, energy, and critical-infrastructure operators.
An OT/ICS assessment with a plan for what to fix
A fixed-scope review of your control environment, starting with architecture, configuration evidence, interviews, and passive capture. You receive:
- An evidence-based asset inventory and current-state network diagram.
- Findings mapped to the frameworks and requirements your operation uses.
- A target architecture and prioritized remediation roadmap.
See the assessment scope and deliverables
I'm Jacob Behnken. My background includes a decade of executive oversight at a regulated pipeline operator, covering infrastructure, SCADA, business continuity, and TSA cybersecurity controls. Read my background.
Services
Assessment & readiness
Independent, vendor-neutral assessments mapped to NIST CSF and IEC 62443, and the regulatory requirements you already answer to.
Network & systems
Architecture review and segmentation design for the SCADA and industrial networks running the operation.
- SCADA and industrial network security
- IT/OT segmentation design and review
- Infrastructure resilience
TSA-designated operators
For TSA-designated pipeline and LNG operators, I prepare the Cybersecurity Assessment Plan and annual report around the evidence from your environment. The engagement includes a three-year assessment rotation and a prioritized list of gaps to address. Your team retains the filing relationship with TSA.
Directives in force
- SD Pipeline-2021-01G
- Enhancing Pipeline Cybersecurity
- SD Pipeline-2021-02G
- Pipeline Cybersecurity Mitigation Actions, Contingency Planning, and Testing
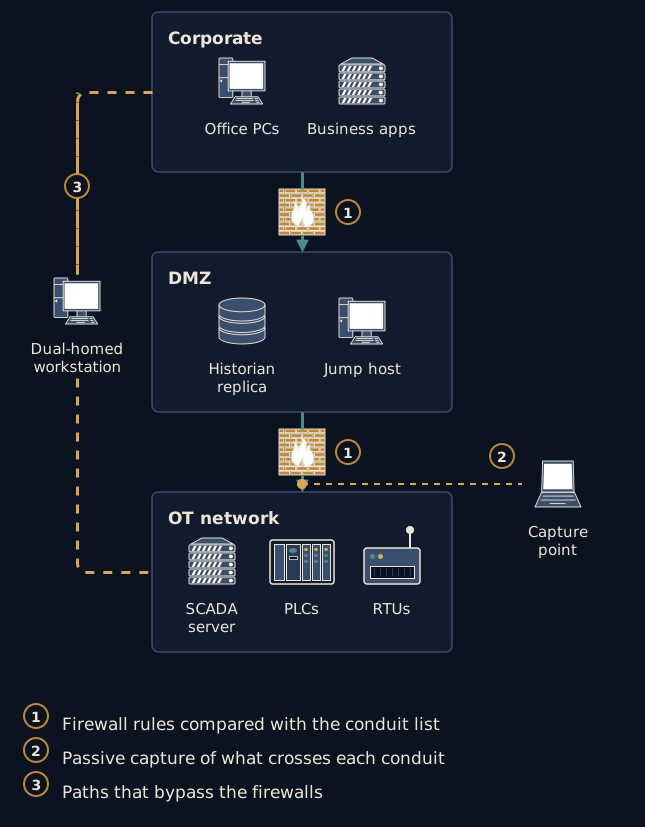
What a segmentation review examines
Firewall rules, observed traffic, and paths around the intended boundary tell different parts of the story. This illustrative diagram shows how the evidence fits together.
See the segmentation review scope
Working references
Field notes
- What is IEC 62443? The OT security standard series explainedIEC 62443 is a series of standards for industrial automation and control system security. What the parts cover, how zones, conduits and security levels work, and who the standard applies to.
- What is NIST SP 800-82? The OT security guide explainedNIST SP 800-82 is the federal guide to securing operational technology. What Revision 3 covers, how it differs from earlier versions, and how operators use it.
Discuss your assessment
We'll discuss your sites, the question you need answered, and the scope of the work. No technical documents needed for the call.
I reply to inquiries within one business day.
Still working out where to start? Take the readiness check.